Secrets
A Secret contains sensitive data such as a password, a token, or a key and it is encrypted at rest. Once a secret has been specified within the DX Engine, its original value cannot be seen again. Secrets are referenced using the secret function within JS expressions. Example: secret('myPassword').
When DX Engine secrets are exported/migrated, only the encrypted values are copied.
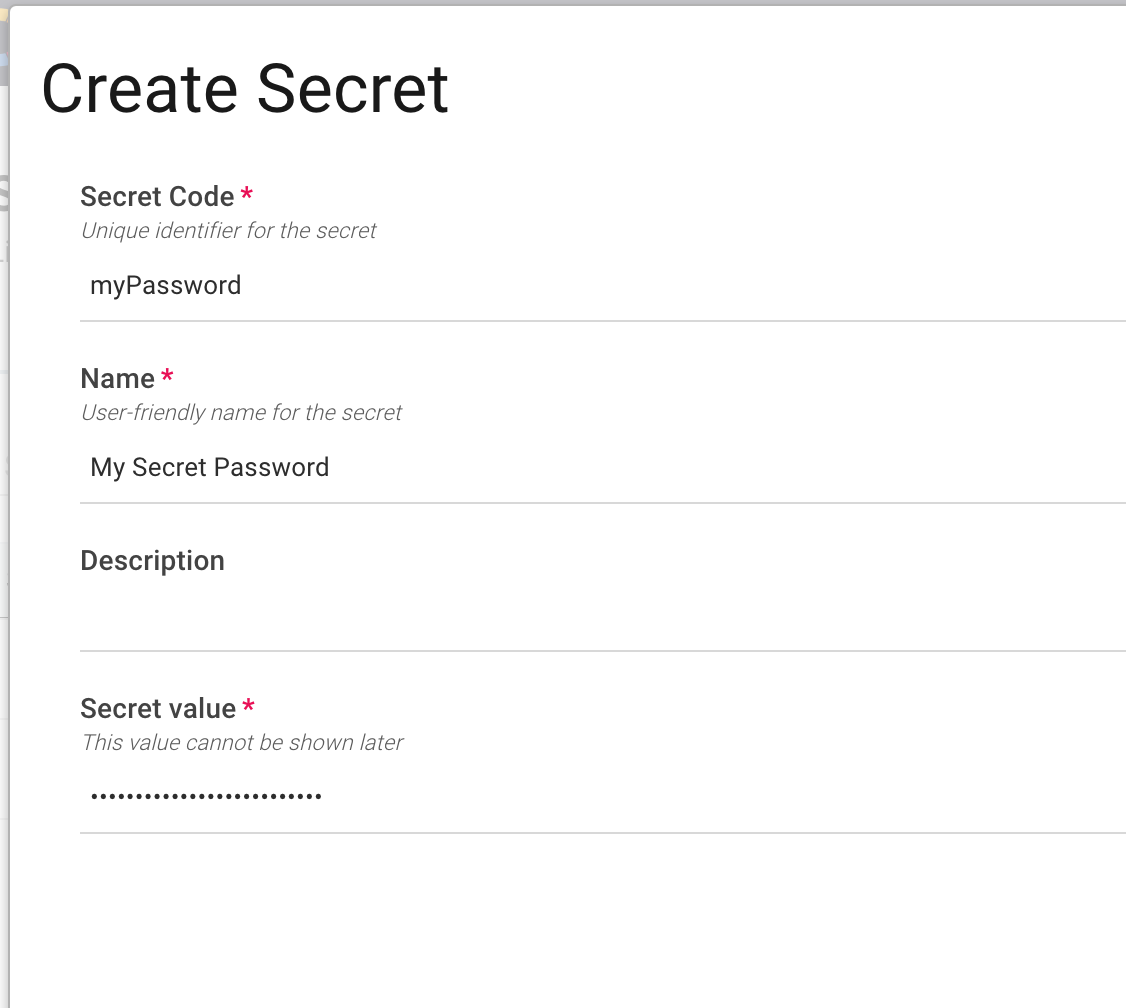
Secrets cannot be accessed from within an Orchestration Component. See Environment Variables for non-secret variables that can be access within Orchestration Components.
Secrets Management API
Create a Secret
POST {{engineUrl}}/experience/secrets
X-Customer-Code: {{customerCode}}
X-Environment-Code: {{environmentCode}}
Authorization: Bearer {{dxEngineToken}}

{
  "secretCode": "myPassword",
  "name": "My password",
  "value": "myPasswordValue"
}
Update a Secret
PUT {{engineUrl}}/experience/secrets/{{secretCode}}
X-Customer-Code: {{customerCode}}
X-Environment-Code: {{environmentCode}}
Authorization: Bearer {{dxEngineToken}}

{
  "name": "My new password name",
  "derscription": "My updated password description"
}
Remove a Secret
DELETE {{engineUrl}}/experience/secrets/{{secretCode}}
X-Customer-Code: {{customerCode}}
X-Environment-Code: {{environmentCode}}
Authorization: Bearer {{dxEngineToken}}